Fortanix has integrated Cloud Native Computing Foundation Confidential Containers into its Confidential AI platform, linking Kubernetes workload attestation with conditional encryption-key release inside hardware-based trusted execution environments to protect data and AI models during inference.
Data security firm Fortanix Inc. extended its Confidential AI platform to support the Cloud Native Computing Foundation’s Confidential Containers project, known as CoCo. The integration bridges a security gap in artificial intelligence deployments.
That vulnerability occurs during model inference when sensitive data and model weights must be decrypted inside processor memory.
Ordinarily, running AI workloads inside standard containers leaves them exposed to privileged administrators and cloud operators who have access to the underlying host infrastructure. By utilizing hardware-based trusted execution environments, or TEEs, the updated platform ensures that memory is encrypted and access is restricted while workloads run.
The system relies on two core Fortanix services working in tandem. The Confidential Computing Manager handles hardware-rooted attestation, verifying both the CPU and graphics processing unit together to ensure the environment is genuine. Meanwhile, the Data Security Manager holds encryption keys and releases them only after successful verification matches the customer’s security policy.
Containers are how the world ships applications, and in the AI era, they’re what makes AI scalable. But moving AI into containers doesn’t change the threat.
Anand Kashyap, Co-Founder and Chief Executive Officer at Fortanix
Kashyap noted that models, agents, and applications continue to touch an organization’s most sensitive data and intellectual property while operating.
That makes zero-trust security essential throughout the process.
Having attestation and key management on one platform spares enterprises from building the trust layer themselves when adopting standard Confidential Containers.
Fortanix Confidential Computing Manager executes this verification, simultaneously authenticating the CPU and GPU so that an inference task encompassing both hardware elements receives complete coverage.
Once these plugins are installed, launching a container within a confidential computing setup requires just a single click across compatible Kubernetes platforms and hardware.
Survey Reveals Enterprise Security Gaps in AI Inference
According to survey data published by Fortanix, 93% of respondents agree that traditional encryption fails to protect data while artificial intelligence is actively processing it.
That fundamental limitation has tangible business consequences.
Security concerns have proved severe enough to cause 41% of surveyed organizations to block an AI deployment completely.
Attestation is a process. Trust is an operation.
Anuj Jaiswal, Chief Product Officer at Fortanix
Jaiswal emphasized that the integration allows teams to adopt standard Confidential Containers without needing to build a complex trust layer from scratch.
The platform is designed for flexible deployment options, supporting software-as-a-service models, on-premises installations, and fully air-gapped environments.
Fortanix offers a Data Security Manager.
Fortanix extends Confidential AI to Kubernetes workloads through Confidential Containers https://t.co/4EHH2HYC9h
That product functions as a key management system combined with a FIPS 140-2 Level 3 hardware security module.
Meanwhile, its Confidential Computing Manager manages hardware-backed attestation specifically for the CoCo runtime.
Fortanix highlighted several key capabilities of the platform, including around-the-clock support, high availability, and compliance certifications covering ISO/IEC 27001, SOC 2 Type 2, and FIPS 140-2 Level 3.
Partners Back Open Standards for Production Scale
A broad alliance of technology companies supports the Confidential Containers ecosystem and Fortanix’s latest release.
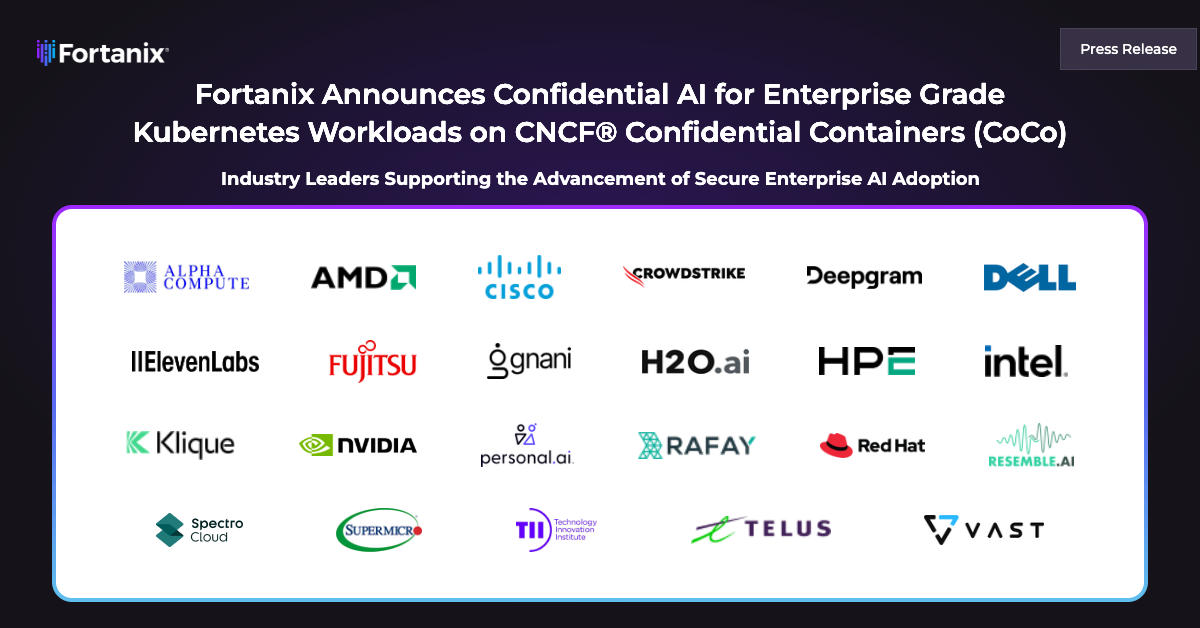
That group includes NVIDIA, Intel, AMD, HPE, Cisco, CrowdStrike, Supermicro, Red Hat, Eleven Labs, Deepgram, Gnani, Resemble AI, Rafay, Spectro Cloud, Telus, and Technology Innovation Institute.
Nvidia, which previously launched a joint on-premises confidential AI platform with Fortanix, views the development as an essential step for scaling secure deployments.
Enterprises need data to stay protected while running models and agents, and labs need the same privacy to protect their models — NVIDIA Confidential Computing keeps both data and models private.
John Fanelli, Vice President of Enterprise Software at Nvidia
Fanelli added that Fortanix is building upon open standards for attestation and secure key release at production scale through ongoing collaboration with the CNCF Confidential Containers community.
"The work @Fortanix is doing within the CNCF Confidential Containers project highlights the power of open collaboration in solving critical security challenges." — Mike Barrett, VP, Hybrid Cloud Platforms @RedHat #NVIDIAGTC https://t.co/WhkaHgcmS4
Deepgram Engineering Kris Efland pointed out that Fortanix’s integration with Confidential Containers adds security layers to existing enterprise Kubernetes environments.
That addition facilitates safer and more scalable deployment of private voice AI.
Additional industry leaders endorsing the secure enterprise AI adoption and collaboration include Alpha Compute, Dell Technologies, Fujitsu, H2O.ai, Klique, Personal AI, VAST Data, and others.
Brittany Kaiser, CEO of Alpha Compute, emphasized that confidential containers backed by Fortanix attestation and key management give proof and help make verifiable sovereign intelligence the default.
Moses Guttmann, CEO and Co-Founder of Klique, noted that their joint architecture offers the cryptographic certainty organizations need to put mission-critical AI into production.
Fortanix Workflow Handles Image Pulling and GPU Validation
Under the technical workflow documented by Fortanix, image pulling and unpacking occur directly inside the confidential guest virtual machine.
The Attestation Agent collects hardware evidence, while the Confidential Data Hub requests secrets only after verification succeeds.
Administrators configuring Intel TDX deployments encounter specific GPU handling choices within the Fortanix Helm chart.
Containers or confidential VMs? Teams shouldn’t have to choose.In this blog, we explain how Fortanix Confidential AI now brings verifiable security to CNCF Confidential Containers at container speed.https://t.co/ylxBkMVnzP#ConfidentialAI #secureai #enterpriseai #aisecurity pic.twitter.com/wlLKONnbZW
Selecting the Required
setting forces the Confidential Computing Manager to validate GPU evidence through Nvidia’s attestation service.
In addition, application registration capabilities for Intel Trust Domain Extensions (TDX) and AMD Secure Encrypted Virtualization-Secure Nested Paging (SEV-SNP) were officially incorporated into the release notes issued by Confidential Computing Manager on September 17.
Fortanix plans to demonstrate its Confidential AI platform on Nvidia GPUs with confidential computing enabled at Nvidia GTC Berlin.