
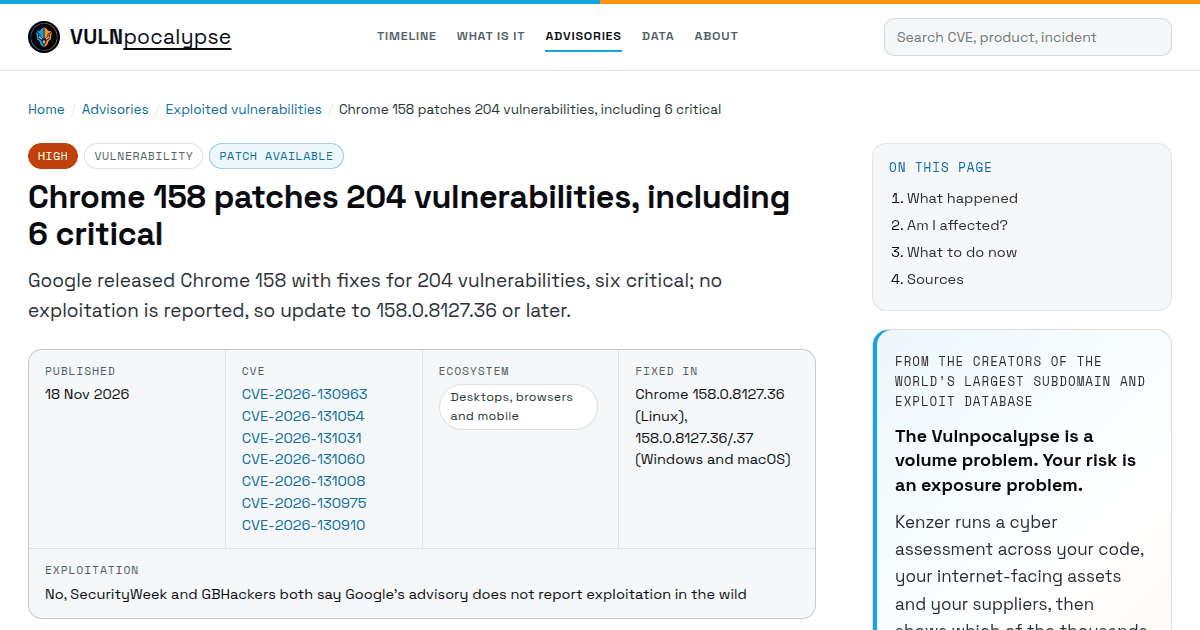
Google released Google Chrome 158 to the desktop Stable channel on Tuesday patching 204 vulnerabilities.
The update arrives for Windows, macOS, and Linux with six critical-severity security issues, according to Cybersecuritynews. The release includes builds 158.0.8127.36 for Linux and versions 158.0.8127.36 or 158.0.8127.37 for Windows and macOS, as reported by HelenTech.
Google began rolling out the update on Tuesday, November 17, 2026. Distribution reaches users over days and weeks. No exploitation in the wild has been reported for any of these security flaws.
Google classified six memory flaws as critical. These cover three use-after-free bugs, two out-of-bounds writes, and a buffer overflow.
The use-after-free vulnerabilities affect WebView under CVE-2026-130963, garbage collection under CVE-2026-131008, and WebAudio under CVE-2026-130975. Graphics and media processing components account for the remaining critical items, including an out-of-bounds write in the GPU component under CVE-2026-131031, an out-of-bounds write in ANGLE under CVE-2026-131054, and a buffer overflow in Media under CVE-2026-131060.
Google did not indicate that any of these security gaps were actively exploited abroad. The company encourages clients to upgrade their software promptly.
The company credited Anthropic’s Xinyang Ge with reporting four of the critical issues. It said Claude assisted on the GPU and Media vulnerability reports. Google reported the WebView and ANGLE flaws directly.
Beyond the critical items, the 204 total fixes break down into 62 high-severity, 82 medium-severity, and 54 low-severity problems. The most common type of vulnerability patched in Chrome 158 is use-after-free with 51 occurrences, followed by incorrect authorization with 34 occurrences, missing authorization with 16 occurrences, out-of-bounds write and read with 15 occurrences, and uninitialized resources with 14 occurrences.
Information leaks account for 11 occurrences, user interface misrepresentation has 10, improper input validation has 9, and race conditions have 8.
Out of all the security weaknesses overall, 163 will not receive any financial payout. No bounty will be issued for the critical bugs.
The tech giant has not yet decided the compensation amounts for 36 flaws. It did hand out $11,000 for five reports submitted by outside researchers.
Google found 145 of those and Xinyang Ge found 15. Alongside the desktop deployment, Google also published version 158.0.8127.42 for the Android version of Chrome on the same day. This will become available on Google Play over the coming days.
Chrome 158 removes native browser support for XSLT processing. This moves XML stylesheet transformation tasks out of the default runtime.
Administrators maintaining legacy internal systems dependent on `XSLTProcessor` APIs must migrate workflows. Alternatively, they can rely on temporary enterprise policies and conditional origin trials running until August 2027, as detailed by 窓の杜.
The desktop browser also introduces the Web Install API alongside USB and Bluetooth HID device support for Android applications. According to SecurityWeek, the corporation chose not to provide any bug reward money for the half-dozen critical flaws, though it did grant $4,000 to Arni Hardarson from Neonix Security in exchange for information regarding CVE-2026-130910, which involves an ANGLE protection mechanism failure marked by high severity.
Users can check for the updated builds by opening the browser menu, selecting help, and opening the about screen to prompt a restart. In managed environments, administrators should check the running version across endpoints rather than treating an available or downloaded update as installed. HKCERT advises visiting the vendor website for details before installing.