Malicious browser prompts mimicking human verification tests trick computer users into running harmful software.
The deceptive ClickFix scam relies on familiar browser verification pages to distribute harmful payloads.
Scammers Trick Users With Fake Verification Prompts
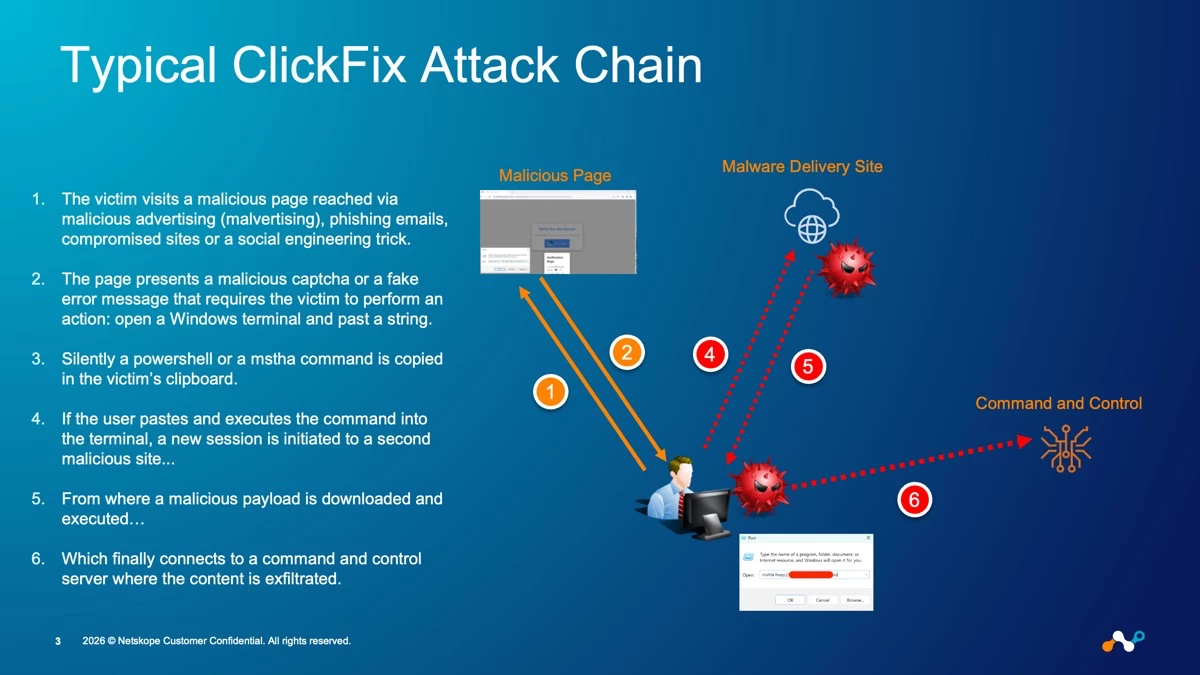
People shopping online are frequently greeted by prompts asking them to verify you are human by completing the action below instead of traditional image selections or text matching.
When an unsuspecting visitor checks a verification box, malicious code copies to their system clipboard. The page then instructs the user with a specific prompt:
“To better prove you are not a robot, please: Press & hold the Windows Key + R. In the verification windows, press Ctrl + V. Press Enter on your keyboard to finish.”
Executing this sequence pastes the hidden commands into the system run window, infecting the computer. Alternative variants warn targets that something went wrong when displaying this webpage before issuing the same harmful instructions.
Chris Fistonich, a researcher with cybersecurity company Malwarebytes, said, “ClickFix is really one of the most sophisticated malware campaigns there is.”
“People are not prepared for this. They are used to solving Captchas every day. They’re used to being able to trust their security software. So it really has opened a new security loophole that’s being exploited extensively,” Fistonich told the Guardian.
He said, “This is the most popular way to get malware on to your computer. Certainly not the only way, but today it is definitely the most popular.”
Attackers Deploy Evolving Payloads
Threat actors continually refine these social engineering methods to deliver diverse payloads, including remote access trojans, loaders, and infostealers, SOC Prime reported.
Recent variants use steganographic delivery and browser-cache-seeded execution chains. Huntress investigations into malvertising, typosquatting, and SEO poisoning campaigns identified attack chains using Node.js-based remote access trojans such as DuskDesk, DLL sideloading with legitimate Microsoft binaries, and PNG steganography to conceal executable payloads.
Security investigations also revealed lateral movement activity targeting domain controllers through native Windows protocols.
Organizations Block Browser Threats
To defend against these threats, security guidance advises that organizations should train users not to paste commands from web pages into terminals or Run dialogs.

Recommended technical controls include application allowlisting, blocking execution from user-writable locations like Temp directories, monitoring for suspicious scheduled tasks or Run keys, and restricting local administrator privileges.
When security teams detect ClickFix activity, response protocols dictate focusing on suspicious behavior sequences rather than relying only on static indicators of compromise.
Analysts should look for web browsers spawning command line interfaces or PowerShell processes, unexpected archive files appearing in temporary directories, and newly created scheduled tasks.
Additional warning signs include unauthorized reverse SSH tunnels and unusual network connections originating from Node.js executable processes.
Because these scams rely on people acting quickly and without thinking through their actions properly, users are advised to pause and consider what they are doing whenever they are online, check their security software, contact their bank immediately if compromised, and change their passwords starting with the most important ones first.