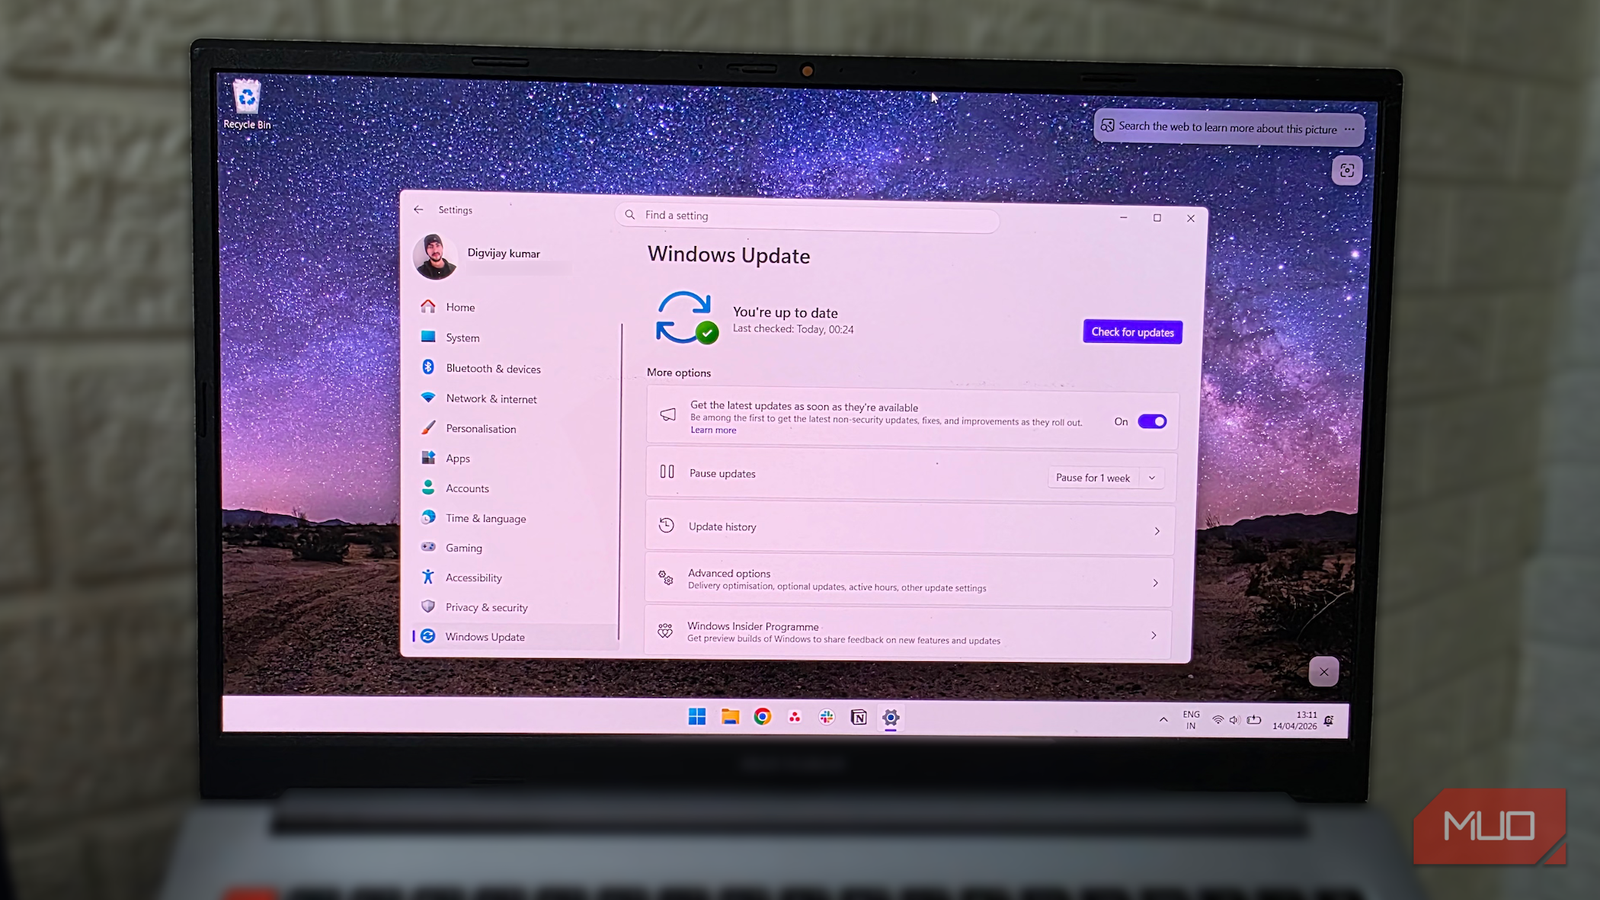
Millions of Windows computers face a disruption in update access as Microsoft rotates digital certificates on May 17 and June 19, 2027. While most supported devices receive the replacement keys through standard monthly updates, unpatched systems risk losing all connection to Windows Update unless administrators take manual action.
A foundational security mechanism keeping Windows devices in touch with Microsoft servers is undergoing a sweeping overhaul. On October 8, 2026, Microsoft published details on the Windows IT Pro Blog regarding an upcoming backend certificate replacement schedule. Devices that fail to receive the updated digital keys before the deadlines will lose the ability to download security patches or feature updates entirely.
Microsoft Replaces Cryptographic Certificates in May and June 2027
When a PC checks for updates, it relies on cryptographic certificates to confirm it communicates with an authentic and trusted server rather than a malicious actor. Because standard cybersecurity practices require these digital credentials to rotate periodically, Microsoft is replacing the existing keys with new counterparts. The transition occurs across two distinct dates: May 17, 2027, and June 19, 2027. Microsoft is highlighting this through multiple avenues, including its own IT Pro Blog post, the Windows Release Health Message Center, and the Microsoft 365 Message Center.

For most everyday users running current, supported operating systems, the change requires zero intervention. The replacement certificates ship quietly inside normal monthly security updates. In most cases, no action is required,
Microsoft stated in its initial guidance, though administrative oversight remains critical for systems that have fallen behind on servicing schedules. This change also follows months after Microsoft began refreshing Secure Boot certificates that were due to expire in late June 2026, marking another routine maintenance milestone after 15 years.
Patch Requirements Vary by Operating System Edition
The specific deadline and required patch level vary depending on the operating system edition installed on each machine. Systems managed through Windows Server Update Services (WSUS) are excluded from the disruption. While standard monthly patches will suffice for the majority of devices, certain Windows releases require direct intervention from IT staff.
| Windows Version | Required Update Level | Expiration Deadline |
|---|---|---|
| Windows 11, version 25H2 and later | None (native support) | N/A |
| Windows 11, version 24H2 and Windows Server 2025 | September 2025 security update or newer | June 19, 2027 |
| Other in-support versions of Windows 11 and Windows Server 2022 | July 2026 security update or newer | June 19, 2027 |
| In-support versions of Windows 10 | July 2026 security update or newer | June 19, 2027 |
| Windows 10 Enterprise 2019 LTSC, Windows Server 2019, and Windows Server 2016 | July 2026 security update or newer | May 17, 2027 |
Home users running Windows 10 outside of an Extended Security Updates (ESU) subscription face the steepest hurdle. Because mainstream support for Windows 10 ended in October 2025, unrolled machines have missed subsequent cumulative patches, meaning they lack the July 2026 update carrying the new certificates. Microsoft extended ESU coverage through October 12, 2027, allowing devices to enroll and catch up.
“However, the key to getting updates from Windows Update beyond 2027 is to keep your devices up to date today,”
Andrew Brown, Microsoft
Manual Remediation Options for Missed Deadlines
If a machine misses the expiration date, standard automatic recovery fails because the device can no longer reach Windows Update to fetch the necessary files. Unsupported operating systems that cannot accept the patches will lose update access entirely and face mandatory upgrades. Machines running outdated editions will be cut off from Windows Update services permanently, leaving an upgrade as the sole official recommendation.
Having hopefully updated the Secure Boot certificates that Microsoft rotated following a 15-year cycle, IT administrators must now manage update channel transitions with that exact same level of care. Determining the exact OS status involves examining version strings composed of four parts, such as 10.0.26200.9457, where the third component represents the OS build and the final segment tracks the Update Build Revision.
- Directly download the required KB package from the Microsoft Update Catalog and install it manually on the affected device.
- Distribute the necessary cumulative updates across the network using regular IT software management tools.
IT administrators can verify device build numbers and servicing states using inspection scripts or by checking the system update history. To confirm eligibility on Windows client machines, users can inspect their build specifications through the system settings interface while ensuring cumulative patches from mid-2026 onward are present.