Global internet infrastructure faces widespread disruption as critical vulnerabilities in the PHP programming language prompt emergency server shutdowns from Germany to the United Kingdom, driven by active remote code execution threats and urgent patch deployments.
Two critical vulnerabilities discovered in the core of PHP have triggered an international cybersecurity alert, forcing universities, hospitals, and government agencies to take web services offline. The flaws, designated under the identifiers CVE-2026-109618 and CVE-2026-109619, carry a severity rating of 9.2 out of 10 according to the PHP security team. Because PHP underpins a vast portion of the digital ecosystem—including content management platforms like WordPress, Joomla, Drupal, and Moodle—the potential surface area for attacks spans millions of servers globally.
Emergency Server Shutdowns Across German Institutions
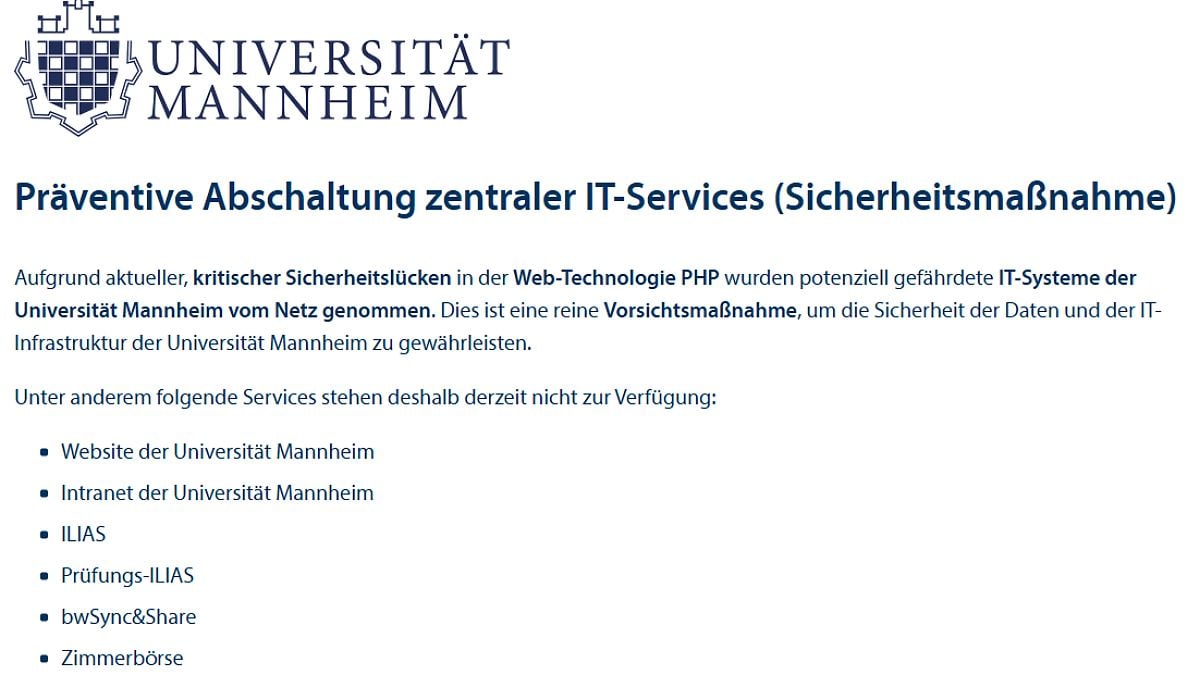
The operational fallout hit digital infrastructure directly in Germany, where public sector bodies and academic institutions moved swiftly to contain the exposure. Official web presences for the state of Baden-Württemberg and the city of Mainz went dark, alongside the online portal for the Charité hospital in Berlin. Temporary outages also affected the Federal Court of Justice and the Federal Ministry for Housing, Urban Development and Building, while university portals such as the University of Mannheim pulled homepages offline as a precautionary measure.
The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2.PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.
The German Federal Office for Information Security, known as the BSI, classified the threat under case number BITS-H Nr. 2026-297981-1032 at warning level 3 / Orange
, signaling an extraordinarily high risk of major disruption to regular operations. To prevent unauthorized infiltration where immediate patching is impossible, the agency advised administrators to consider a temporary disconnection of the web server from the internet until the patch is deployed.
IT experts strongly advise contacting responsible system administrators, IT service providers, or web hosting providers immediately. Available patches and security updates for the PHP environment and utilized content management systems must be implemented without any delay.
PHP sites behind Cloudflare already have an initial set of WAF rules deployed for the known exploit vectors in these vulnerabilities. The rules are available to all customers, including free.We are seeing early attacks emerging and are updating mitigations as new vectors show… https://t.co/wMz9tDTWwH
From Hacker News Leak to Coordinated Global Warning
The public alarm began on October 20, 2026, when a Hacker News user under the pseudonym petecooper published details regarding two critical remote code execution flaws, claiming an initial disclosure schedule set for October 22. Security researchers at watchTowr investigated the claims and successfully verified the existence of the vulnerabilities. Prompted by the premature leak and emerging threat data, The PHP Foundation issued an advance advisory ahead of its standard schedule.
An early advisory is being issued by the PHP security team regarding an upcoming security release scheduled for Wed, Oct 21st 2026, 14:00UTC, which addresses two critical vulnerabilities, both rated CVSSv4 9.2.PHP users are encouraged to prepare to update.

European cybersecurity bodies mobilized quickly following the alert. The European Union cyber agency, CERT-EU, recommended applying official remedies immediately upon release while temporarily isolating unpatched assets, a stance echoed by the National Cyber Security Centre in the United Kingdom, which advised organizations to take vulnerable systems offline if quick remediation proved unfeasible. For example, like the EU services, the UK’s National Cyber Security Centre also advises organizations to update immediately to protect themselves from critical PHP flaws.
Cloudflare Deploys WAF Rules to Block Active Exploitation
The race to secure servers intensified as infrastructure providers detected hostile activity before official software updates became publicly available. Cloudflare reported observing the first active exploitation attempts against the vulnerabilities.
The NCSC is encouraging UK organisations to prepare for immediate updating of systems using PHP. Where immediate remediation is not feasible, organisations should consider taking the system offline until it can be fully mitigated.For more⬇️ https://t.co/l6TDtVurJN
For known exploit vectors associated with these flaws, websites powered by PHP that use Cloudflare now benefit from a newly deployed initial set of WAF rules. The rules are available to all customers, including free.
While network-layer mitigations provide an initial defense shield, security analysts emphasize that edge protection serves only as a temporary buffer and cannot replace core application patches. With updated packages released by developers on Wednesday afternoon, system administrators face a compressed timeline to upgrade legacy installations and protect backend databases against potential data extraction.