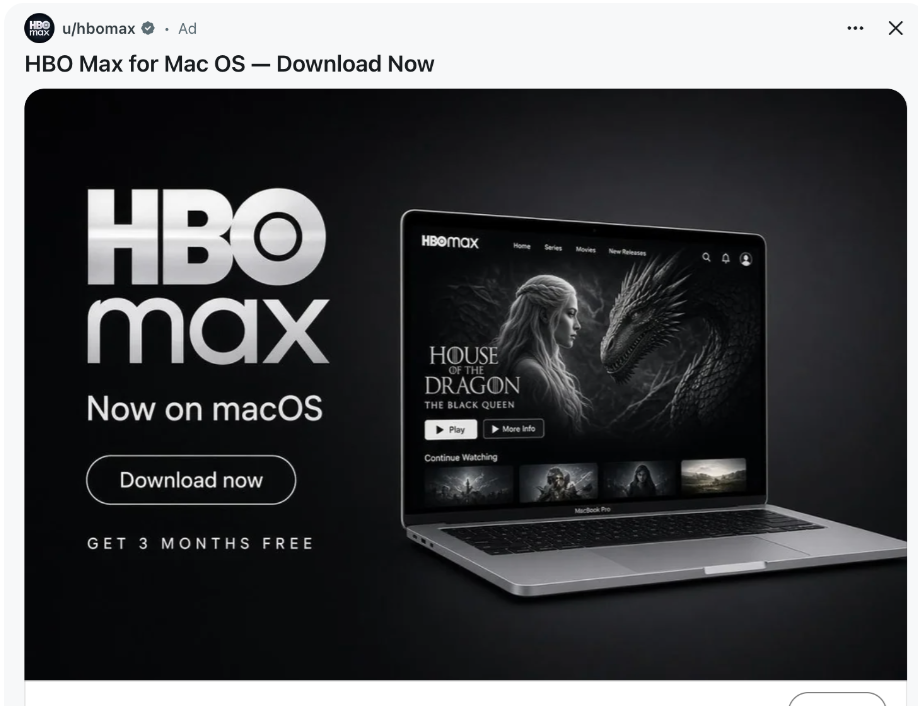
In September 2026, the official HBO Max Reddit account was compromised to distribute 108 malicious ads over 48 hours, using a “ClickFix” social engineering tactic to trick users into executing terminal commands that installed information-stealing malware on macOS and Windows devices.
The compromise of the verified HBO Max Reddit account (u/hbomax) in September 2026 exposed users to a massive malvertising campaign that leveraged social engineering to distribute malware. Over 48 hours, the hijacked account pushed 108 distinct advertisements, some of which redirected users to fake landing pages designed to mimic official HBO Max branding. These ads prompted users to copy and paste terminal commands, a tactic known as “ClickFix,” which bypassed standard browser protections and infected devices with information-stealing malware.
The Malvertising Blitz and Its Tactics
The campaign, dubbed “PasteSwitch” by researchers, utilized multiple lures to maximize its reach. Advertisements targeted users seeking streaming services, AI tools, and macOS utilities, with domains such as hbomaxx[.]app and codex-craft[.]com. The malicious payloads included macOS stealers, Windows loaders, and fake cryptocurrency wallet applications. One of the most alarming aspects of the attack was the use of blockchain-based command-and-control (C2) infrastructure, which allowed threat actors to dynamically rotate domains and evade takedown efforts.
According to research by Hudson Rock and ADAMnetworks, the attackers exploited the verified status of the HBO Max account to bypass user skepticism. A Reddit user first flagged the suspicious ad, which claimed to offer a native macOS application for HBO Max—a service that does not exist. The ad directed users to a landing page that mimicked official branding, then triggered a “ClickFixprompt requiring terminal commands to install the software.
The classic infostealer/clickfix paste this command to download,” the user noted in a subreddit post, which was later verified by cybersecurity analysts.
Reddit confirmed it paused the affected ads and initiated an investigation into the account compromise. HBO Max’s parent company, Warner Bros. Discovery, did not immediately respond to inquiries about the breach. The campaign’s scale was revealed through OSINT tools, which tracked the rapid rotation of domains and the variety of software lures used. Researchers observed 36 mainnet changes to the C2 infrastructure between March and July 2026, highlighting the attackers’ ability to adapt and persist.
Why ClickFix is a Growing Threat
ClickFix attacks rely on social engineering to trick users into manually executing malicious commands, making them particularly effective against both casual and technical users. Unlike traditional malware, which often exploits software vulnerabilities, ClickFix leverages user trust in legitimate platforms. The campaign proves once again why trusted distribution channels are becoming prime targets for infostealer delivery,
said Alon Gal, co-founder and CTO of Hudson Rock, in a LinkedIn post.

Researcher Kevin Beaumont emphasized the risks of such tactics, noting that running commands in system terminals is not a routine action for most users. A request to paste unknown text into a system tool should be treated as a serious warning sign,
he wrote. The attack’s success underscores the need for heightened awareness, especially as threat actors increasingly target verified accounts to exploit their credibility.
The PasteSwitch campaign also demonstrated the growing sophistication of malware delivery. On macOS, payloads like MacSync and AMOS Helper were used to exfiltrate browser credentials, Telegram data, and macOS passwords. Fake cryptocurrency wallet applications, such as those mimicking Ledger and Trezor, were deployed to steal BIP39 recovery phrases. These techniques align with broader trends in cybercrime, where attackers prioritize stealth and persistence over brute-force exploitation.
Unresolved Questions and Ongoing Investigations
While Reddit and cybersecurity researchers have taken steps to mitigate the attack, several critical questions remain unanswered. The exact number of users who clicked the malicious ads and the total number of infected devices are still unknown. Additionally, the method by which the HBO Max account was compromised—whether through phishing, credential theft, or another vector—has not been publicly disclosed.

For users, the incident serves as a stark reminder of the risks associated with clicking on unfamiliar links, even those appearing to originate from trusted sources. Reddit has since paused the affected ads and is working with security teams to investigate the breach. As the cybersecurity community continues to monitor the situation, the incident underscores the evolving nature of malvertising and the importance of vigilance in an increasingly digital world.