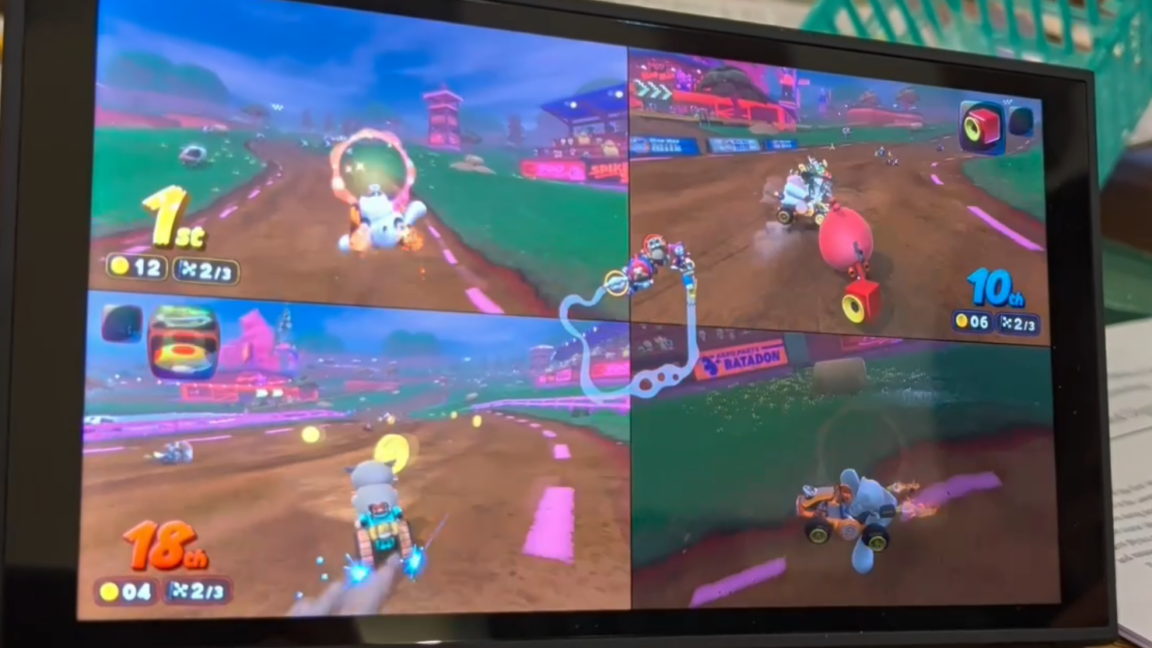
Security researchers have unlocked the Nintendo Switch 2 using a software-only tethered jailbreak named ns2jb. Operating on system version 23.0.1, the exploit chains a 32-bit integer overflow in SmileBASIC 4 with a filesystem service vulnerability, allowing homebrew execution and game modifications without hardware alterations.
The Nintendo Switch 2 was expected to resist early software breaches, but it has encountered its first public software-only jailbreak a little over a year after its initial release. Sammy Hajhamid, a Caltech undergraduate and security researcher who publishes online as pepsipu, created the exploit. He distributed the exploit chain on GitLab under the designation ns2jb along with its complete source code.
This bypass relies entirely on software routines running on system firmware version 23.0.1 across both the Switch 2 and the original console. It differs from traditional hardware modifications. Those require physical tampering or soldering.
i jailbroke the nintendo switch 2so i modded cinnamoroll, peter griffin, hatsune miku, and more into Mario Kart World, a switch 2 exclusivenow watch my friends and i get cooked by botslearn more and get the exploit https://t.co/ykjgyfrFRp pic.twitter.com/BOcFhejRz1
Researcher Gezine reviewed Hajhamid’s methodology and provided independent validation. Gezine previously published a separate Switch 1 and Switch 2 userland exploit in July.
The codebase allows users to run unsigned homebrew code at system-module privilege levels. Users can also perform save data backups and execute ExeFS spoofing by replacing retail game executables with modified versions.
People seem to be confused about this.I meant that there’s an exploit based on a physical game cartridge.So you don’t have to update the firmware to use the eShop. https://t.co/qsRBHbyNtu
Hajhamid designed the framework deliberately without game-backup execution capabilities to exclude piracy. It provides access to memory-mapped I/O peripherals and single-player modding tools for owners who keep their systems disconnected from the Nintendo Network.
OpenAI Codex Automates Exploit Discovery
Hajhamid used artificial intelligence automation to speed up vulnerability discovery. He constructed an automated physical testing rig. He paired two JetKVM units to capture HDMI video output and send USB commands. He also added a Bluetooth light-switch mechanism to physically press the console power button during crashes.
This apparatus allowed OpenAI Codex to test inputs around the clock for roughly two weeks.
The process focused on SmileBASIC 4. This programming environment was initially released for the original hardware. It maintains backward compatibility on the newer platform via the eShop ecosystem.
Joining the effort to push the Nintendo Switch 2 jailbreak further. Coffee brewed, terminal open, curiosity unbounded.See you on the other side of the sandbox.#Switch2 #Jailbreak #Homebrew #ReverseEngineering pic.twitter.com/OBEwJim8qC
SmileBASIC 4 Contains Integer Overflows
Codex located a 32-bit integer overflow within array-removal operations inside the BASIC interpreter.
Tethered Exploit Limits Functionality
The developer reports that the framework enables save file backups and homebrew program execution within userland parameters, beyond game modifications.
I guess it's the right time to burn this (to be paired with smilebasic or other game)https://t.co/nTcXN9AREA pic.twitter.com/mG2fA2he1i
Operational constraints restrict practical deployment. The exploit is tethered. This means the system requires a local network connection to a macOS or Linux computer running a Node.js package to re-apply the payload after every reboot.
It does not provide permanent custom firmware installation or kernel-level control over core system operations. It requires version 4.4.9 of the prerequisite application and approximately 20MB of free save space.
Talked with this guy.Seems legit.Also he knew what was my userland exploit (different with what he posted)So I will post it in github in few days. https://t.co/ExxGnODnsZ
Nintendo Pulls SmileBASIC 4 From Store
Nintendo removed SmileBASIC 4 from its digital storefront worldwide following public disclosure of the exploit chain.
This mirrors a 2016 precedent. Earlier iterations of the same programming application were pulled from the Nintendo 3DS eShop after being utilized for firmware exploits prior to corrective system updates.
Users engaging with modified hardware risk enforcement actions. This includes provisions that reserve the right to remotely brick consoles found running unauthorized software.
Industry analysts expect firmware patches to arrive shortly, but corporate representatives have not issued formal public statements regarding the security breach as of publication.