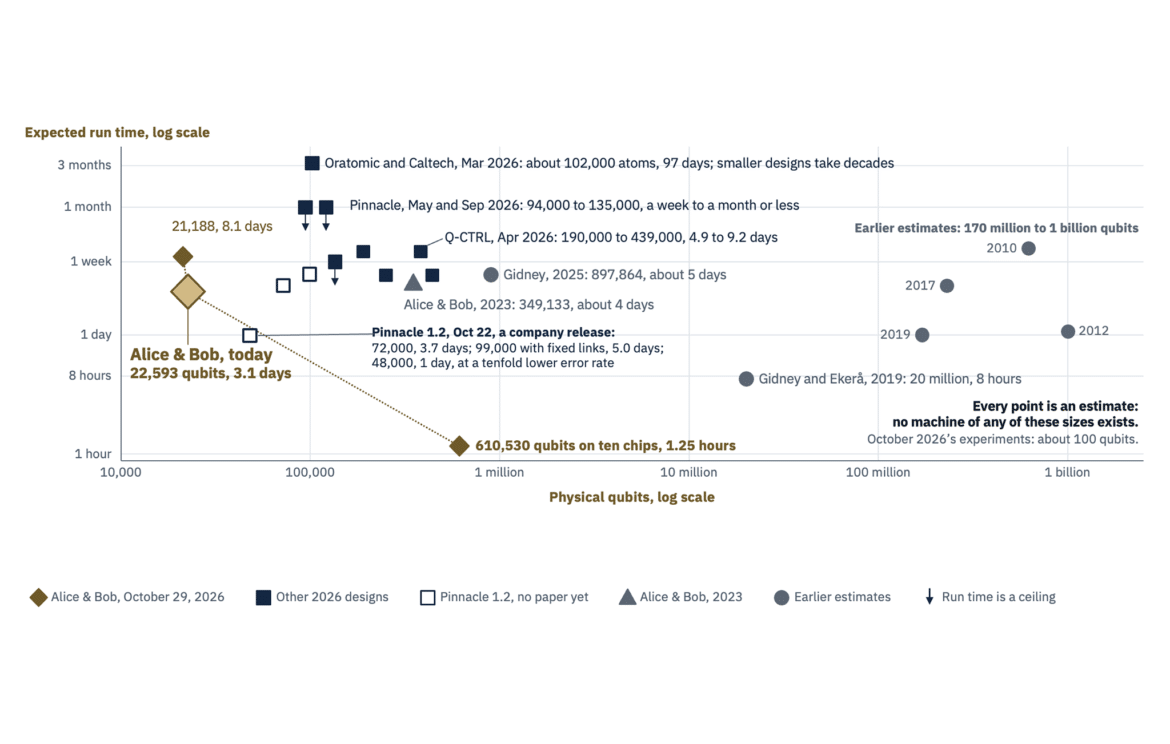
Quantum researchers at Alice & Bob have published a resource estimate concluding that a superconducting quantum computer requires 22,593 physical cat qubits to break RSA-2048 encryption in 3.14 days, alongside a separate configuration targeting Bitcoin’s elliptic-curve cryptography in just over an hour.
The Paris- and Boston-based quantum computing developer Alice & Bob released its findings in a 122-page preprint dated October 23 and posted to the IACR Cryptology ePrint Archive. The research targets secp256k1, the elliptic curve underpinning Bitcoin signatures, calculating that an attack would require no more than 29,588 physical qubits and take 61.8 minutes. Nine of the paper’s ten authors are company researchers, with Axel Pappalardo and Dahmun Goudarzi sharing first authorship, alongside André Schrottenloher of Inria.
Alice & Bob Compile Shor’s Algorithm for RSA-2048 and Bitcoin Keys
The new estimates mark a steep drop from earlier calculations by combining more efficient error-correction codes with refined implementations of Shor’s algorithm, the quantum computing method introduced in 1994 by mathematician Peter Shor to factor large integers and solve discrete logarithms. In 2019, Craig Gidney of Google Quantum AI and Martin Ekerå estimated breaking RSA-2048 would demand roughly 20 million physical qubits. By 2025, Google brought that figure below one million physical qubits.
French quantum company @Alice__Bob estimates that 22,593 qubits could break RSA-2048 in about three days. It is the smallest estimate I have seen that runs in days. But it needs qubits nobody can build yet. The paper is serious work. The team laid out Shor's algorithm qubit by…
The company utilizes superconducting cat qubits designed to suppress bit-flip errors directly in hardware, leaving error correction to handle only phase-flips. That architectural choice reduces the physical qubit count required behind each error-corrected logical qubit.
Researchers Contrast Cat Qubits With Google Quantum AI Estimates
The new resource figures highlight distinct engineering philosophies when compared to Google Quantum AI’s research. While Google’s March whitepaper outlined an approach requiring fewer than 500,000 physical qubits that could derive a single wallet’s private key in about nine minutes once a public key appeared, Alice & Bob’s balanced configuration demands roughly 17 times fewer physical qubits while accepting a longer runtime.
| Configuration | Physical Qubits | Runtime |
|---|---|---|
| Alice & Bob (RSA-2048) | 22,593 | 3.14 days |
| Alice & Bob (Bitcoin secp256k1) | 29,588 | 61.8 minutes |
| Google Quantum AI (March whitepaper) | Fewer than 500,000 | About 9 minutes (if primed in advance) |
The architectural differences mean the two studies rely on separate hardware designs and operational assumptions. Alice & Bob’s estimates assume bit-flip times of approximately a century; introducing a bit-flip roughly once an hour would raise the RSA-2048 qubit requirement from 22,593 to about 45,000.
New research from quantum computing firm Alice & Bob estimates that a error-corrected quantum computer with ~29,600 physical quantum bits could crack the 256-bit elliptic curve cryptography that secures Bitcoin private keys in just ~61.8 minutes 📊This is just a theoretical…
Bitcoin Security Faces Threats From Hour-Long Attack Timelines
The hour-long attack timeline exceeds Bitcoin’s average block interval of roughly 10 minutes, meaning transactions in progress remain protected while awaiting block confirmation. However, coins associated with addresses that have already exposed their public keys face a direct vulnerability because attackers would not need to finish the calculation before the next block forms.
Alice & Bob urged organizations to start moving to post-quantum cryptography now.
Google previously identified more than 1.7 million BTC held in Pay-to-Public-Key scripts, an early address format leaving public keys visible on-chain, while other tracking estimates put the total pool of coins behind exposed public keys at more than 6 million bitcoins. To mitigate this exposure, developer Jameson Lopp and five co-authors have advanced BIP-361, a proposal to freeze quantum-vulnerable legacy addresses in phases.
Hardware Roadmap Targets the Early 2030s for Deployment
Despite the theoretical progress demonstrated by the preprint, building a fault-tolerant quantum computer at this scale involves an enormous engineering hurdle. Alice & Bob’s own hardware development is currently far from the 30,000-qubit mark; results published on October 20 for the French government’s PROQCIMA quantum program relied on three demonstrators, with the largest operating on a 12-qubit chip whose logical error rate was not yet below the error-correction threshold.
Alice & Bob put breaking RSA-2048 at 23,000 cat qubits and three daysIn 1994, mathematician Peter Shor showed that a sufficiently large quantum computer could break RSA and the elliptic-curve cryptography behind Bitcoin.#googlequantumai pic.twitter.com/Q5EjNEYz43
Company leadership expects hardware advancements and falling resource requirements to converge in the early 2030s, aligning with an internal roadmap targeting a 100-logical-qubit machine named Graphene by 2030. In the interim, executives argue that institutions must begin transitioning to post-quantum cryptography immediately given the lengthy operational runways required to secure global infrastructure.
Quantum computing firm Alice & Bob estimates that 29,588 physical qubits could crack ( bitcoin:native ) Bitcoin’s public-key cryptography in approximately 62 minutes, requiring roughly 17 times less hardware than Google’s earlier benchmark near 500,000 qubits. The models use… pic.twitter.com/SQsOICIKtM
The source is this Alice & Bob paper (posted Oct 28 2026):https://t.co/gNh8mFUCIdIt estimates at most 30,000 cat qubits and ~1 hour to solve ECDLP on secp256k1 (Bitcoin’s curve) under their assumptions. The 62-minute figure is a close approximation of that 1-hour estimate. No…