Apple has introduced Reference Image, a new opt-in camera mode for the iPhone 18 Pro and iPhone 18 Pro Max announced on September 9, 2026. The hardware-tied feature captures signed sensor data at the moment of capture, developing an unalterable digital negative via Private Cloud Compute to help verify authenticity.
How Hardware-Level Signing Creates a Secure Digital Negative
As generative tools make it increasingly simple to alter or manufacture photorealistic pictures, standard metadata systems have struggled to maintain a reliable chain of custody. Traditional approaches relying on the C2PA standard attach provenance metadata only after capture, leaving the editing chain vulnerable to compromise.
Apple is addressing this vulnerability by moving verification directly into the physical components of the device. The system relies on custom-designed image sensors built into the main camera of the iPhone 18 Pro and iPhone 18 Pro Max. When a user activates the opt-in Reference mode, the camera sensor signs every pixel it sees at the exact moment the shutter is pressed.
The cryptographic journey begins the moment the sensor is initialized during manufacturing. The hardware generates a signing key pair, keeping the private key secure while the public verification key is recorded in the device hardware manifest. That private key binds the pixel data to that specific sensor before the image ever reaches iOS for further processing.
Private Cloud Compute and the Verification Pipeline
Because raw sensor values require extensive computational processing like demosaicing and lens-shading correction to become viewable, simple sensor signing is not enough on its own. Apple solves this by routing the signed data through Private Cloud Compute, an audited cloud infrastructure designed to perform verifiable algorithmic operations without exposing data.
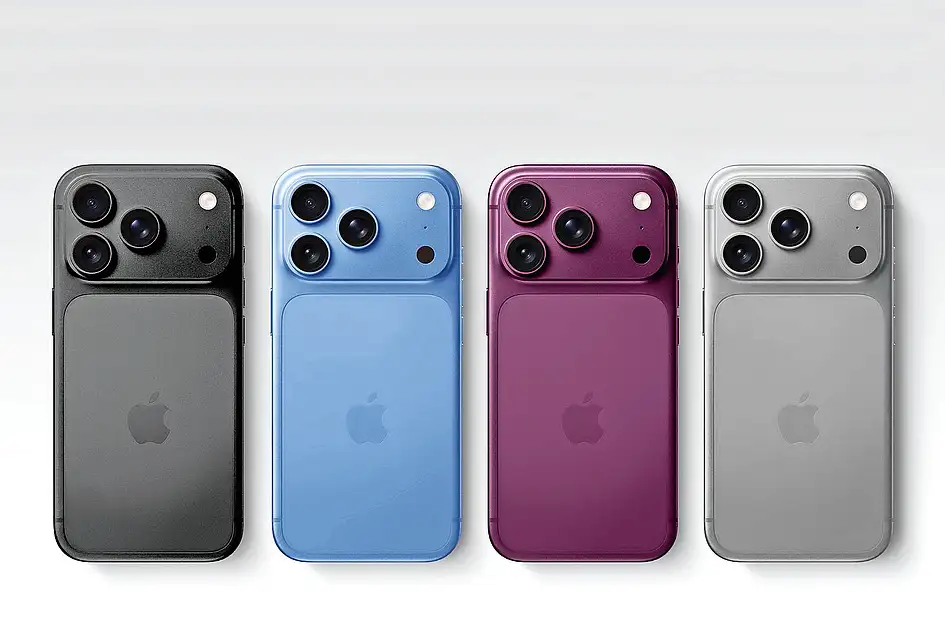
Once the signed sensor data reaches Private Cloud Compute, the system verifies the sensor signature and cryptographic timestamps. After running these checks, the infrastructure processes the data into an unalterable reference image resembling a secure digital negative.
This final reference image is signed using a combination of traditional and post-quantum cryptography. The framework is deliberately designed so that outside observers cannot identify the photographer, the device used, or whether two reference images came from the same phone.
“the only image provenance system that provides quantum-secure defenses.”
Apple, Security Research
Using Reference Images in Photos and Third-Party Apps
For everyday users, the workflow centers on the Photos app. When a photo is captured in Reference mode, the resulting reference image is stored alongside the standard version. Users can view the assets side by side to determine whether subsequent edits, crops, or AI manipulations were applied to the visible picture.

The capability extends beyond Apple’s native software. Apple is releasing dedicated application programming interfaces across iOS 27, iPadOS 27, and macOS 27. These APIs allow third-party developers to integrate reference image inspection directly into their own applications.
The feature forms part of a broader authenticity strategy. Later this year, a software update will introduce support for Google DeepMind’s SynthID standard to help identify AI-generated or edited files, though the company stresses that a reference image is evidence of capture history rather than a universal detector for every image circulating online.
Pricing, Regional Rollout, and Launch Limitations
However, global availability varies significantly depending on regional regulations.
Apple has confirmed that photo capture using Reference mode will not be available at launch in China due to regulatory requirements. European Union users face a similar restriction on initial capture functionality on the new hardware, though users running the iOS 27, iPadOS 27, and macOS 27 software updates will still be able to develop and view reference images locally.